Rubber Ducky

--Originally published at Stories by Dennis Kingston on Medium

A month ago, on our course of Security, some classmates made a presentation about a USB that could take control of your computer in less that a second. I found it pretty interesting and that is why I’m going to talk about the Rubber Ducky.

Nowadays, is very important to know that USB’s are becoming an important weapon for cracking. This is why you need to have precautions when plugging in a USB to any computer. (It can be a Rubber Ducky)

The Rubber Ducky is a coded keyboard that once it is plugged in, it starts writing whichever commands were coded, on the terminal in order to have permissions to files, and in those movements, start listening to everything you do on your computer.

Finally I would like to remark that security is very important and we should make people more conscious about this subject, because I think there are a lot of people that don’t know this basic concepts and could lead them to be cracked and maybe lose information or be stolen their personal info.

If you want to know more about the Rubber Ducky: https://hakshop.com/products/usb-rubber-ducky-deluxe
Let’s talk about Bitcoins!

--Originally published at Paco's adventures

Hey everyone! I’m sure a lot of you have heard about the bitcoins and how are increasing and decreasing in value and that some people or countries are already using them or even banning them, but, Do you really know how they work or what exactly are? Do you know how to obtain them? Is it really safe to invest on them? Well, I’ll try to give you all this answers and also some data of bitcoins related to security.

First, What are bitcoins? Bitcoins are a descentralized cryptocurrency, follow up question: What is a cryptocurrency? It is a digital currency that uses cryptography to secure and verify transactions and also for the creation of more units.

Resultado de imagen para bitcoin

That’s a good explanation but I will add more to it. Bitcoin is digital money that it has no real value in real life (like gold or bills), just the believe that they have some other value in products. But how does it operate? Well there are a group of people in the bitcoin network, the maintainers, who have a copy of the ledger (book of financial accounts), and they are in charge of making sure the transactionsare correct and not a fraud. Each transaction has the amount, the accounts from where and to who is going that transaction and also a signature encrypted to make sure is the real person doing the transaction and not a fake account, each transaction has their own signature.

To make sure all the maintainers have the same ledger, all of them vote… with MATH! That’s right, they pull a math problem and the first who solve it, and also has a record of multiple problems solved, becomes the “leader” and everyone follows its ledger.

When they solve a problem, and also there is a fee for Continue reading "Let’s talk about Bitcoins!" →

What was my password again?

--Originally published at Paco's adventures

Hello everyone! How you doing? Sorry for not uploading in a long time but now I’m back so let’s get to the main topic: Passwords, more specifically, remembering passwords and reusing them in different pages and accounts.

I’m gonna be honest, I’m really bad at creating and remembering different passwords for my accounts whether it’s for games, job, school or Netflix. Not only that but I usually use the same password with some variations like numbers, special characters and more.

giphy

Also, if I want to use a completely new password I write it down in a note where my other passwords are, and also my usernames, and I leave it on my desk. But then, if I don’t remember my username or password and I’m out, I’m basically screwed. Maybe there are people out there with a problem like mine, well in that case I found or rather my classmates and my teacher gave me a great solution: LastPass.

Resultado de imagen para lastpass

This is a great tool and it had helped me a lot. It is a password manager service that can be use in your web browser and what it does is that you create your account and you get you master password, after that when you enter your username and password for Youtube, Facebook, etc. your password gets locally encrypted. After that, not only you don’t have to type again both of them to enter, LastPass remember them and it doe sthe job for you.

Not only that but it also has a security test where it compares all your passwords in all the accounts and tells you how strong or weak are and how many times you repeat it how similar are they to others so you can take action and change them. When I did the test the first Continue reading "What was my password again?" →

Upgrade your dependencies!

--Originally published at miguel.net

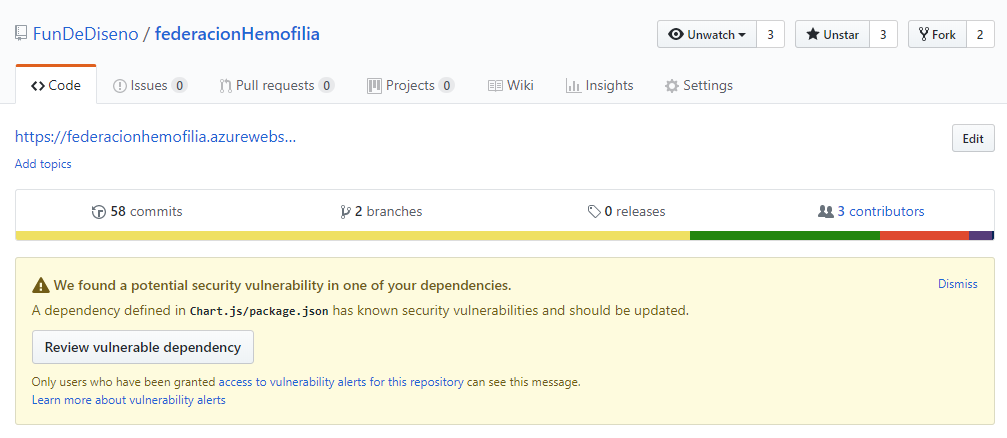
I recently revisited and old repository on my public GitHub, and I was impressed on how good is the platform, as soon as I was on the repository, I was checking I was received by a big yellow banner alerting me on a dependency vulnerability.


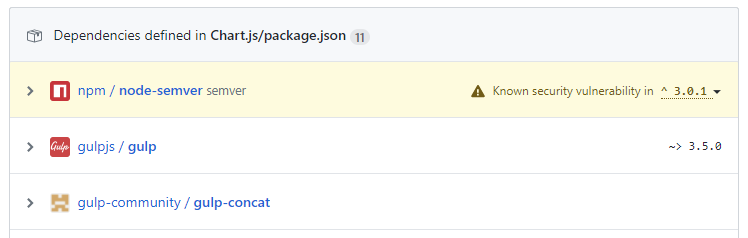
One of my JS dependencies is vulnerable! but when I checked the vulnerable dependency, I was surprised by how the vulnerability is really hitting me.


It is a dependency of one of my dependencies, and then I just started wondering, how may other packages or systems can be affected by things like this! It is not just a dependency, it is a dependency I trusted because I trusted on Chart.js.

Now, ASP.NET Core is one framework I use a lot, and .NET Core is the runtime on which it runs, since it is now open source, I decided to take a look at their announcement repository, just to know if they have something where they tell everyone about a known security issue. To my surprise, they do have a tag of security, and they are continuously updating it, on the .NET repository as well in the ASP.NET repository.


So, now lets take a look at one of those issues, Elevation of Privilege is a common attack on windows systems, so having those kind of problems on a server in a cloud platform seems like a bad idea, lets take a look at the most recent Issue. And to my surprise, it is very well documented, it has all the necessary info about which software is affected and how to be safe, which versions of the runtime or packages are already patched so you can update to those ones.

Conclusion
As maintainers of our own services, we should be aware of this kind Continue reading "Upgrade your dependencies!" →

Public Wi-Fi networks

--Originally published at miguel.net

I love visiting different places to eat, like restaurants or small business that serve great food, and beer. As part of my weekly visit to one of those places, I found that their Wi-Fi router was vulnerable to one of the most common and easy attacks, getting into the administrative panel and do what ever you want, because the password was the default!

The process
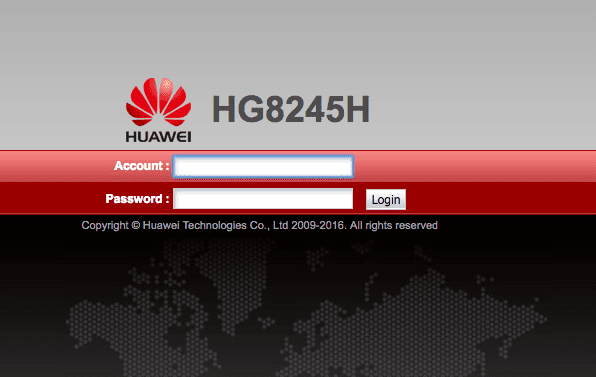
First, I got the Wi-Fi password, which was cleverly written on a whiteboard on the wall in front of me. After login in, I just checked which was my default gateway and proceed to enter the address in my browser. And I got this page:

Resultado de imagen de hg8245h login page

Then I did what any person with minimum search skills could do, just searched for the default login password and username for that specific modem, which was cleverly publish on this website.


I entered those default username and password and boom! I was in, just got access to the full administrative panel of a place where they have a computer for accepting payments, where Rappi or Uber eats can place orders, and also where they use a terminal to make charges to credit and debit cards.


After that I immediately told my waiter that I needed to talk to the manager, then he showed up and I explained to him what I did, and how easy it is to find those kind of things, he completely understood the problem and fixed it by the next day with some help, and he offered me a beer for the finding, so everyone was happy at the end of the day.

Conclusion
This wasn't my first experience with a problem like this, and I also tried to reach some managers from other places with this problem, some of them seems to not be Continue reading "Public Wi-Fi networks" →

Cryptography

--Originally published at Computer and Information Security

The concept of cryptography can be easy to understand, but not as easy to implement. Cryptography has been around a while now. Today, we hear that word and we imagine a secure program to protect passwords, but it was mainly used for war. First of all, we can define cryptography as an activity to convert an intelligible text into an unintelligible one or all the way around. This method is used to protect information and its main goal is to send and receive this plain text decoded in order to decode it. It is also used for authentication.

cryptography_magnifyingglass_code_l.jpeg

The first implementations of cryptography were different compared with the modern ones. Today, cryptography is based on pure complex mathematical approaches. The main goals of it are discussed all over the internet, but the most controversial ones, at least for me, are following ones:

  • Confidentiality: confidentiality means that no one can understand the encrypted message but the receiver and only using the tools to decode the message.
  • Integrity: it is crucial that no one can be able to alter or modify the integrity of the encrypted message.
  • Non-reoudiation: this means the the one that is sending the message cannot deny the content of the message at a later stage. There can’t be differences between what is send and what is received.
  • Authentication: authentication can be used to confirm the connection between the one that sends the message and the one who receives it.

There are a lot of advantages regarding cryptography. Banks, computer passwords, and e-commerce transactions use it to protect their information from getting leaked. It is important to say that an encrypted text doesn’t mean that it isn’t crackable, but there a re different ways to measure the effectiveness of an encryption. Normally, they are measured with the amount of Continue reading "Cryptography" →

Cambridge Analytica Data Mining on Facebook, supporting Trump Campaign

--Originally published at Security – Carlos Rueda Blog

Cambridge Analytica, a data analytics firm is under fire for the ilegal mining of user data from Facebook profiles between 2014-2015. The company was revealed to journalists working for the Observer to have used personal information taken without authorization in early 2014 to build a system that could profile individual US voters. The purpose of this was to target Facebook users with personalized political ads.

Facebook itself confirmed the harvesting of information on an enourmous scale. However, at the time it failed to alert users and took only limited steps to recover and secure the private information of more than 50 million individuals.”

Cambridge Analytica themselves had contracted another company to obtain user data, this company being Global Science Research. Analytica says that once they found out that GSR had not obtained the user data in line with Facebook’s terms of service, they deleted all the information that was provided by GSR. The statement went onto say that “No data from GSR was used by Cambridge Analytica as part of the services it provided to the Donald Trump 2016 presidential campaign.”

Facebook updated this statement on the March 17, adding: “The claim that this is a data breach is completely false. Aleksandr Kogan requested and gained access to information from users who chose to sign up for his app, and everyone involved gave their consent. People knowingly provided their information, no systems were infiltrated, and no passwords or sensitive pieces of information were stolen or hacked.”

Cambridge Analytica was created in 2013 by american multi-millionare Robert Mercer, one of Trump’s main supporters. It is claimed that with the deceive of using the database for academic purposes, through russian-american psychologist Aleksandr Kogan, the company obtained permission to ask for user data through an application that claimed to be a Continue reading "Cambridge Analytica Data Mining on Facebook, supporting Trump Campaign" →

Phishing phish.

--Originally published at Merino is talking about security.

Phishing refers to the act of masquerading as a company or institution in order to steal information, such as usernames, passwords, and credit card details.

I presented this subject in class, and to be honest is quite a tricky one. The interesting thing about phishing is that, even if it occurs within the different communications technologies, the attacker doesn't actually need any technical knowledge about technology. The attack happens at a human level, so the attacker doesn't need to be a hacker per-se, they'll just send you an e-mail, pretending to be a company or something, saying that something is wrong with an account of yours, and they need your password to fix it. As easy as that.

The more intricate phishing scams will require technical/hacking skills, like hosting a fake websites online, with a url that's almost indistinguishable from the real deal (only different by a couple of characters, they added 'the', different extension, etc.), where users "log in", or at least they think they do, and actually give away their credentials to attackers. A recent example is what happened with the giant company Equifax because, not satisfied with having a massive security breach, they linked on Twitter to a phishing site. If a large company can be fooled, what about the rest of us. Thats why we always check, and double check the URL var.

But examples like the one above are just the tip of the iceberg, as I wrote above, attackers don't need to be technical experts, they just need to get in contact with you through an email, social media message, even phone calls.  We need to smart about protecting ourselves, if you someone approached you on the street asking for your email and/or password, even if he/she claimed to be from Continue reading "Phishing phish." →