Microservices == Microhell

--Originally published at miguel.net

Microservices, a word that has been buzzing around a lot, every one is writting, speaking and developing under the microservices mindset, but it is never that simple, just splitting a service into small pieces and having them interacting over the wire can cause a great mess.

Not having a good planning on how the service will interact, can cause an auto DDoS, because all the services are too chattie and then overload the network, so essentially, you performed an DDoS attack just by trying to run your system, congratulations.

So, what to do?
Now that the naive solution (http) is discarted, how can you interact in a system where everything is logically separeted? Many solutions have evolved throught out the years, one of the best solutions, specially if you need one way communication, is using a queue service, where messages can be posted and they can be received from the other end of the queue to be proccessed.

RPCs (Remote Procedure Calls), this method of executing actions is sometimes slow, depending on the level of concistency been used, two-phase commit is very costly but is very effective.

During the 80's and 90's, a paper was show, called SAGAS, which described long running transaccions on databases, and how to utilize them to make long queries work efficently, now it had evolved into Distributed SAGAS, a pattern where each microservice is a task, and a sequence of tasks is transaccional, so when an update occurs, every service that needs to be updated will receive the info. Also I really like the idea of a "pipeline" for this kind of situations, for example, maybe a reservation site allows you to book a flight, pay your hotel and rent a car on the same website, at the same time, so then, based Continue reading "Microservices == Microhell" →
Become the hackerman of your router

--Originally published at Paco's adventures

This post is for you to experiment with your router. Maybe you know, or don’t, but you can access your router and change stuff like the name of your network, the password and also the password to access the router. To enter the router you first need its IP address, which you can find in the properties of the network you are connected. After you enter that IP address in a web browser you will be in a log-in page and here is where the fun begins (It’s something like this):

Resultado de imagen para router login

If you check the manual of your router it will tell you that to access it you write something like “admin” or “root” as username and “password” or “admin” for the password, this is the default setting of the router, and you should/must not leave it like that, why? because if someone want to be a bad person, they can enter and modify the things I wrote at the beginning.

You can check the brand of your router in the internet and you will find a page that tells you the default username and password to access it, so it’s not difficult for someone (hacker) to find out and do bad things to your network.

But why am I telling you all of this? Well it’s because of a friend’s story: He went to a place where sell buffalo wings, he saw that the place had wi-fi and just for the heck of it he checked if their router was secure, and oh surprise, it wasn’t he could’ve done anything he wanted, but he is a really nice guy and told the owner the problem and even help him fixed it. Now, almost every place I go (restaurants, bars, shops, etc.) I try to enter their router so Continue reading "Become the hackerman of your router" →

Threats for online gamers

--Originally published at Information Security A01229898

Hi everyone, While I was searching about video games I found about this threats that could happen for gamers, I took this information from a post of we live security esset, so let’s start this.

The first popular threat is TeslaCrypt:

it was designed to encrypt game-play data for dozens of video games, prompting the user to pay a ransom to decrypt those files. Targeting some well-known games including Call of Duty and Minecraft, Teslacrypt blocks access to saved game files, configuration files or game items.


Second one is Password Stealers:

Just as there are types of spyware called keyloggers, which capture keyboard events and try to steal access credentials, there are also pieces of malicious code that attempt to steal access credentials for online games or platforms, such as Steam or Origin. This type of malware is heavily based on social engineering or deceit in order to infect its victims. One of the most popular scams is when a player – the victim – receives a chat message from another player offering him to join his team. This unknown player is usually very friendly and praises the victim for his gaming skills, telling him that he should join this team of great players.

At some point, the victim is prompted to download and install an application – for example, a voice communication program. The attacker will be very insistent on the fact that the victim cannot become part of the team if he does not have that application. And of course, the downloaded executable is not really a chat client, but a malicious software capable of stealing account credentials.

The third one is Fake Game Cracks

This is another social engineering technique, regardless of the kind of threat installed in the end. The deceit in this case has to do Continue reading "Threats for online gamers" →

Security and Videogames

--Originally published at Information Security A01229898

Hi everyone, On this post I will talk about Security and videogames, yes, finally something about software, so let’s start this.


On this post as I mention I will talk about videogames, I was searching on internet and I found a post from welivesecurity esset and they talk about this topic, they interview Andres Rossi the CEO of an Argentine company that develops videogames for social networks, so I grab some information of that post so you can know a little of what they talk and at the end of the post I will put the link so you can check all the post of esset

Andres told that with his experience he has seen a lot of incidents related with security like payment-card frauds, cyberattacks targeting gamers and the subsequent claim of prizes, to exploitation of servers just for the sake of playing, but he says that the most common problem is that players leave their accounts open in machines that do not belong to them. He said that there is a lot of ignorance among video games developers regarding security implementation and one example is that the online Playstation platform was compromised a few years ago, the problem is that there are so many games that, as is to be expected, the challenge is still only focused on the largest and most famous game companies.

At last, I want to say that the security problems that the video game industry it’s because on the past, the industry didn’t need to take care for security, because all games were offline, so, it was not possible to extract information of other players, but with the online games the problem started but is difficult to try to secure all games.


Link of the interview: https://www.welivesecurity.com/2016/08/16/security-transversal-issue-video-games-development/

Master Key for hotels

--Originally published at Lord Security

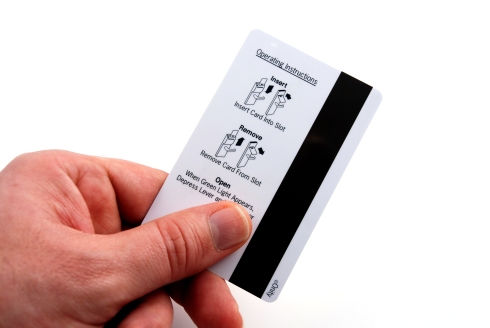
There are may things someone takes i count to select a hotel to stay, the luxury, wifi connection, pool, air conditioner and many others. but something really important is that your stuff remains safe, knowing that no one can enter without your permission, including the cleaning staff.

Blog-Post-3-Photo-1.jpg

That is why a new exploit discovered by F-Secure researchers is important,  a vulnerability in a popular and widely used electronic lock system (Assa Abloy) that can be exploited to unlock every locked room in a facility


For this hack, the attacker needs access to any target hotel key, even though it isn’t from a room or it has expired. Then he would need a portable programmer with a custome code they created, it is hold near the lock to open and in a minute it will be unlocked.


The researchers, for obvious reasons didn’t released the code for the master key and, in fact, showed the findings to the affected company. With Assa, the worked for over a year to recently release an update that fixes the problem

References:

https://thehackernews.com/2018/04/hacking-hotel-master-key.html

Researchers Find Way to Create Master Keys to Hotels

I2C

--Originally published at Information Security A01229898

Hi everyone, on the other post I talk a little about some protocols, but I want to talk more about I2C, so let’s start.

As I explained on the other post I2C means  Inter-Integrated Circuit and it is a synchronous, multi-master, multi-slave, packet switched, single-ended, serial computer bus invented in 1982 by Philips Semiconductor (now NXP Semiconductors). It is widely used for attaching lower-speed peripheral Integrated Circuits to processors and microcontrollers in short-distance, intra-board communication.


I2C uses only two bidirectional open-drain lines, Serial Data Line (SDA) and Serial Clock Line (SCL), on the SDA the master and the slave will send and receive information and the SCL is the clock that the master provides, that clock will determine the velocity of the the transmission.

The bus has two roles for nodes: master and slave:

  • Master node – node that generates the clock and initiates communication with slaves.
  • Slave node – node that receives the clock and responds when addressed by the master.

The bus is a multi-master bus, which means that any number of master nodes can be present. Additionally, master and slave roles may be changed between messages (after a STOP is sent).

There may be four potential modes of operation for a given bus device, although most devices only use a single role and its two modes:

  • master transmit – master node is sending data to a slave,
  • master receive – master node is receiving data from a slave,
  • slave transmit – slave node is sending data to the master,
  • slave receive – slave node is receiving data from the master.


So this is a little of I2C, but the real question on this post is, WHY ARE YOU TALKING ABOUT COMMUNICATION PROTOCOLS ON MICROCONTROLLERS IF THIS A INFORMATION SECURITY POST?

The answer is easy, I’m an electronic engineer and I have more knwoledge of microcontrollers, I don’t work too much with software and don’t Continue reading "I2C" →

Communication protocols

--Originally published at Information Security A01229898

Hi everyone, on this topic I will talk a little about Communication protocols, this topic is related with microcontrollers, because I’m talking about the communications protocols that microcontrollers use, I’m not going to talk about all the communications protocols, so let’s start.

-CAN: I know that I talk about CAN in other post, in fact, I have a post that talks only talks about CAN, but it is a important protocol and I think that I should mention it.

CAN is a protocol that in short words, is a bus, it has two cables and that’s it, it doesn’t have any security, so once your are in, you can know everything and technically you can interfer the system, if you want to know more about CAN protocol you can check my post of CAN and there I explain more and there’s a video that explains more.

-UART: Universal Asynchronous Receivert Transmitter (UART)  is a computer hardware device for asynchronous serial communication in which the data format and transmission speeds are configurable. The electric signaling levels and methods are handled by a driver circuit external to the UART. A UART is usually an individual integrated circuit used for serial communications over a computer or peripheral device serial port. One or more UART peripherals are commonly integrated in microcontroller chips.

-I2C: Inter-Integrated Circuit (I2C) is a synchronous, multi-master, multi-slave, packet switched, single-ended, serial computer bus invented in 1982 by Philips Semiconductor (now NXP Semiconductors). It is widely used for attaching lower-speed peripheral Integrated Circuits to processors and microcontrollers in short-distance, intra-board communication.

-LIN: Local Interconnect Network (LIN) is a serial network protocol used for communication between components in vehicles. The need for a cheap serial network arose as the technologies and the facilities implemented in the car grew, while the CAN bus was too expensive to implement for every component in the car. European car manufacturers started using different serial communication topologies, which led to compatibility problems.


There are other protocols that I could Continue reading "Communication protocols" →

Clean your shoes before entering the house.

--Originally published at Merino is talking about security.

Data sanitization is a simple yet effective tool to preventing attacks. What kind of attacks? you may ask, well many, but all can be summarised as code injection.

In web applications you may encounter with a form, any form, that lets you write whatever string and maybe do something with it, display it as a comment, save it in the data base, send it as message, etc. But lets say that instead of jut plain text, I write a piece of code, and if the input isn't sanitized the page will run that code, and the results can be disastrous. Let the people at computerphile explain it better: 
there are quite some kinds of code injection but here as the most common ones:

SQL injection: As the name indicates, is meant to attack SQL databases, adding sql scripts to the un-sanitized input can result in the database running said queries and returning data that should be read by the user. More info.

Javascript and HTML injection: By adding Javascript and HTML code to un-sanitized inputs can cause the browser to run and make the page behave in unwanted ways, this can potentially affect other users ass well. More info.

A simple solution to this problem is input sanitization, it cleans your inputs so that malicious code can't be written into it. You can do this by preventing certain characters or sets of characters to be typed in your input. Maybe banning the single quote or the <> brackets. The people at eSecurity Planet wrote a very in depth article on how to protect your web applications using code sanitization, there are many things you can do. Since HTML5, input type can be added to any input tag, and that can be a small step into making sure that the incoming Continue reading "Clean your shoes before entering the house." →

Microservices == Microhell

--Originally published at miguel.net

Microservices, a word that has been buzzing around a lot, every one is writting, speaking and developing under the microservices mindset, but it is never that simple, just splitting a service into small pieces and having them interacting over the wire can cause a great mess.

Not having a good planning on how the service will interact, can cause an auto DDoS, because all the services are too chattie and then overload the network, so essentially, you performed an DDoS attack just by trying to run your system, congratulations.

So, what to do?
Now that the naive solution (http) is discarted, how can you interact in a system where everything is logically separeted? Many solutions have evolved throught out the years, one of the best solutions, specially if you need one way communication, is using a queue service, where messages can be posted and they can be received from the other end of the queue to be proccessed.

RPCs (Remote Procedure Calls), this method of executing actions is sometimes slow, depending on the level of concistency been used, two-phase commit is very costly but is very effective.

During the 80's and 90's, a paper was show, called SAGAS, which described long running transaccions on databases, and how to utilize them to make long queries work efficently, now it had evolved into Distributed SAGAS, a pattern where each microservice is a task, and a sequence of tasks is transaccional, so when an update occurs, every service that needs to be updated will receive the info. Also I really like the idea of a "pipeline" for this kind of situations, for example, maybe a reservation site allows you to book a flight, pay your hotel and rent a car on the same website, at the same time, so then, based Continue reading "Microservices == Microhell" →
Not even your car is safe!

--Originally published at Paco&#039;s adventures

Maybe you have noticed that the cars are getting more advanced in their technology, this is great, or is it? More technology doesn’t always mean better or more secure. Of course I’m talking about this from the perspective of informatics, right know most of the cars have bad, or not even have security against hackers. But, why is this an issue? How can this happen? and what are the big companies going to do? Well, let me tell ya!

First, How can someone hack a car? I’ll try to be as simple as possible with the explanation. A lot of the computers used in the cars control things like the brakes, air conditioner, stereo, lights, the gearbox, etc. Mostly all the cars use a bus network to connect each of the computers. Something like this:

In a network like this, you just need to access one of the computers to see what the other computers are doing, and usually there is not a lot of security inside the bus. It has been proved that a lot of ports in the computers are left open for no reason and the hackers can exploit them. Things like the bluetooth and the wi-fi inside the car doesn’t have security. Here is an example of cars hacked (Volkswagen and Audi):

https://www.bleepingcomputer.com/news/security/volkswagen-and-audi-cars-vulnerable-to-remote-hacking/

And if you look for yourself, there are more examples of other cars being hackable. All of this is an issue, a big one, because as I said before, they can control things like the breaks and the gearbox, the hackers can cause an accident making it seem like it was your fault and also it would untraceable, in my opinion the companies should slow down their car releases and start making sure their cars aren’t easily hackable, thankfully they are Continue reading "Not even your car is safe!" →